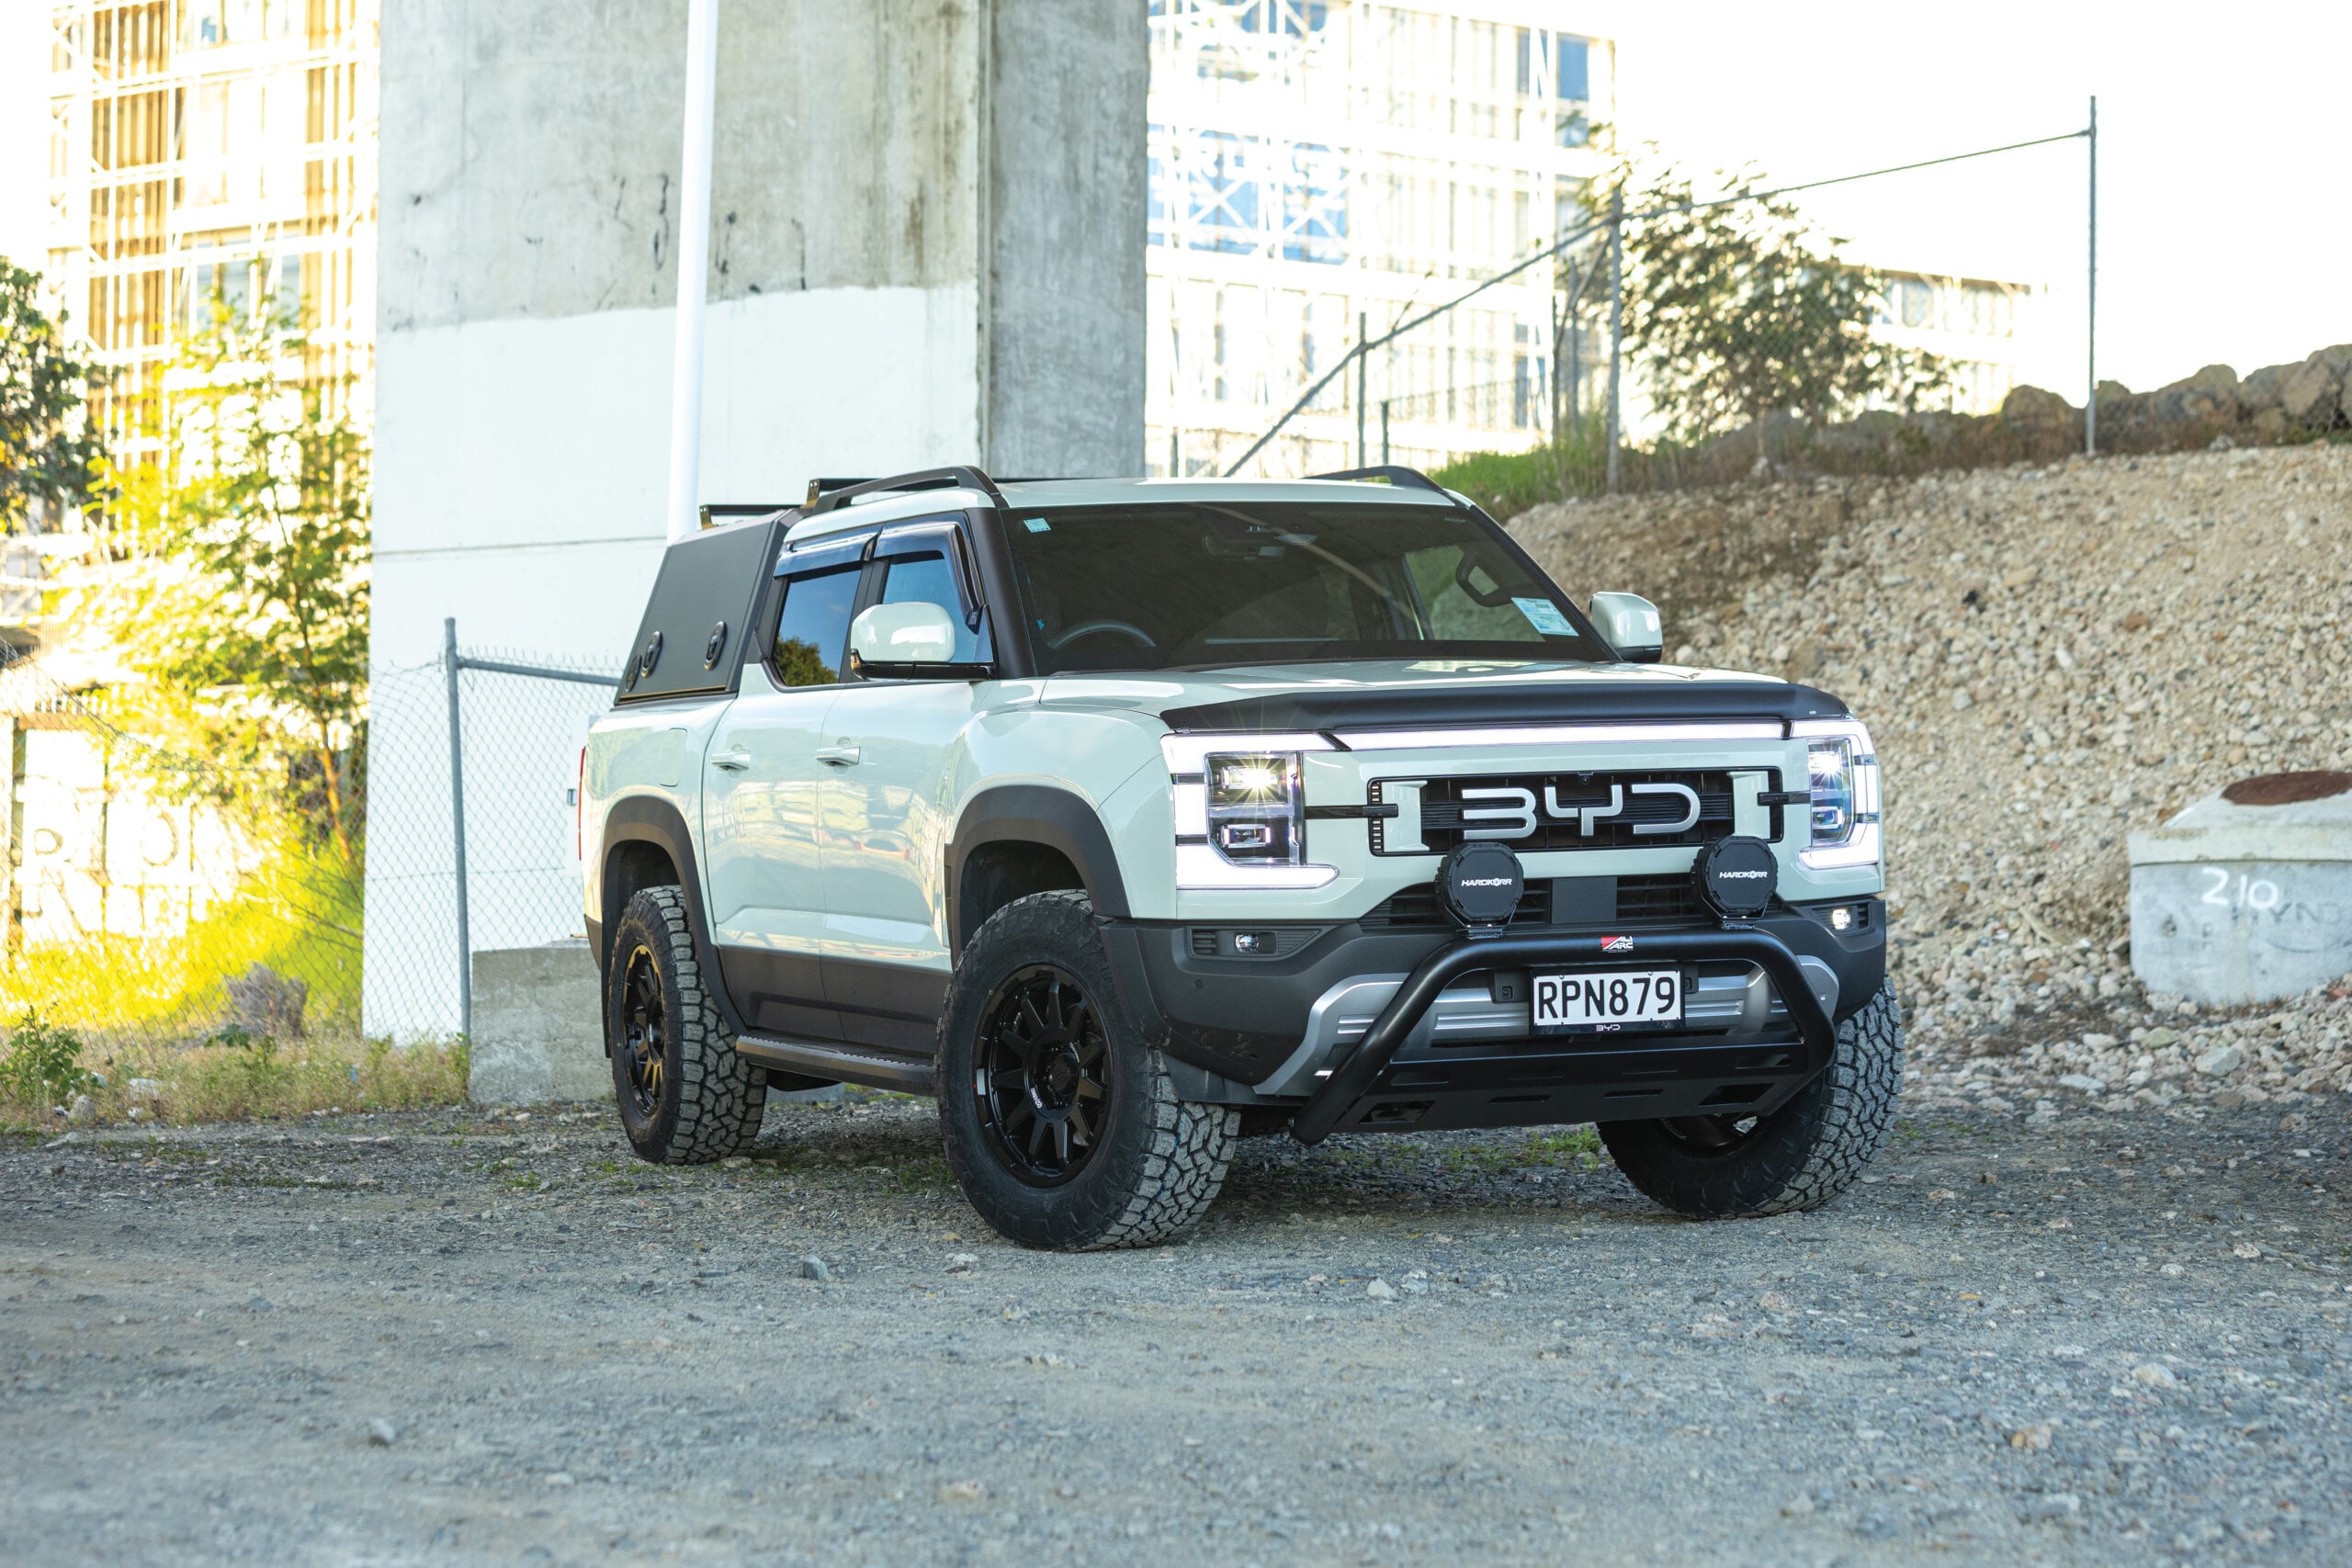
BYD confirms Shark 6 software fault after TV hack, fix coming over the air
Words: Richard Edwards
BYD has confirmed a software defect in the Shark 6 infotainment system that allowed a security researcher to install an untrusted app, and says it will fix it with an over-the-air update.
The response follows an ABC Four Corners investigation broadcast in Australia on September 21, in which Dan Hreszczuk of Canberra-based Fortify Labs demonstrated control of several functions on a Shark 6. The programme reported he could lock the doors, run the wipers and washers, switch the headlights, play content on the screen, record audio through the cabin microphone and track the vehicle’s location. It also reported he could not reach more critical systems such as the brakes and cameras, and that he had the ute for two weeks to develop the attack.
BYD Australia and New Zealand says its investigation, involving technical teams in Australia and China, looked at two separate routes into the vehicle.
The first was the infotainment system’s Android Debug Bridge (ADB), a standard Android development tool that BYD says is switched off in production vehicles. BYD says the researcher exploited a software defect to turn ADB on and install a third-party app, and that its engineers have reproduced both steps.
It says that when the app asked for access to functions such as location or the microphone, the infotainment system displayed a permission prompt that had to be approved manually on the screen.
The second route was the CAN bus, the network that carries messages between the vehicle’s electronic systems. BYD says control of the headlights and windscreen wipers required tapping directly into the vehicle’s wiring.
“This method requires physical intervention on the target vehicle and is limited to the individual vehicle that has been physically accessed,” the company says.
BYD says any external device trying to reach the same network without cutting into the wiring would have to go through the OBD diagnostic port, which uses device authentication and physical isolation and meets UN R155 cybersecurity requirements.
The company has completed a root-cause investigation into the ADB defect. The fix will close the path that allowed ADB to be enabled through the infotainment screen and will be sent to Shark 6 vehicles in a future over-the-air update once it has been validated. Owners will not need to visit a dealer. BYD is also checking whether other models it sells need the same update.
A separate risk assessment will look at whether further protection is needed for messages on the CAN bus.
BYD vehicles are distributed in New Zealand by Ateco, and 219 Shark 6 utes were registered here in September. BYD has previously told us the personal data its connected vehicles send is limited to the VIN, email address and login details, held on servers in Australia.